Capability 01
AI Security
Test the full AI system: models, data, tools, and permissions. Identify where an attacker can change behavior, expose information, or cross a trust boundary.
- Threat modeling
- Adversarial testing
- AI guardrails
Cybersecurity
We test how adversaries move through your systems, help stop active intrusions, and build defenses around the way your mission operates—from enterprise infrastructure to AI-enabled workflows.
Cyber capabilities
Assess a system before deployment, test defenses against a real attack path, or bring in support during an incident. Start with the problem your team needs to solve.
Capability 01
Test the full AI system: models, data, tools, and permissions. Identify where an attacker can change behavior, expose information, or cross a trust boundary.
Capability 02
Trace exploitable paths across applications, identity, cloud, and infrastructure. Test your defenses against adversary behavior and verify what an attacker can actually reach.
Capability 03
Establish what happened, contain the intrusion, and guide recovery. Work from host, identity, cloud, and network evidence to understand the scope of a compromise.
Capability 04
Prepare the people, procedures, and controls that a response depends on. Exercise decisions, close detection gaps, and make remediation part of daily operations.
Connected capabilities
A security finding can expose a code defect, a missing detection, or a question that needs research. Our teams work across those boundaries—from reproducing the problem to building and testing the fix.
Cyber operations
Reproduce the weakness, identify what an attacker can reach, and test whether your defenses catch it.
Explore Cyber operationsEngineering
Address the underlying code, integration, or platform problem. Build the controls and telemetry needed to operate securely.
Explore EngineeringApplied research
Develop repeatable tests for new systems and AI-enabled workflows. Measure failure modes, control effectiveness, and known limits.
Explore Applied researchTechnical work
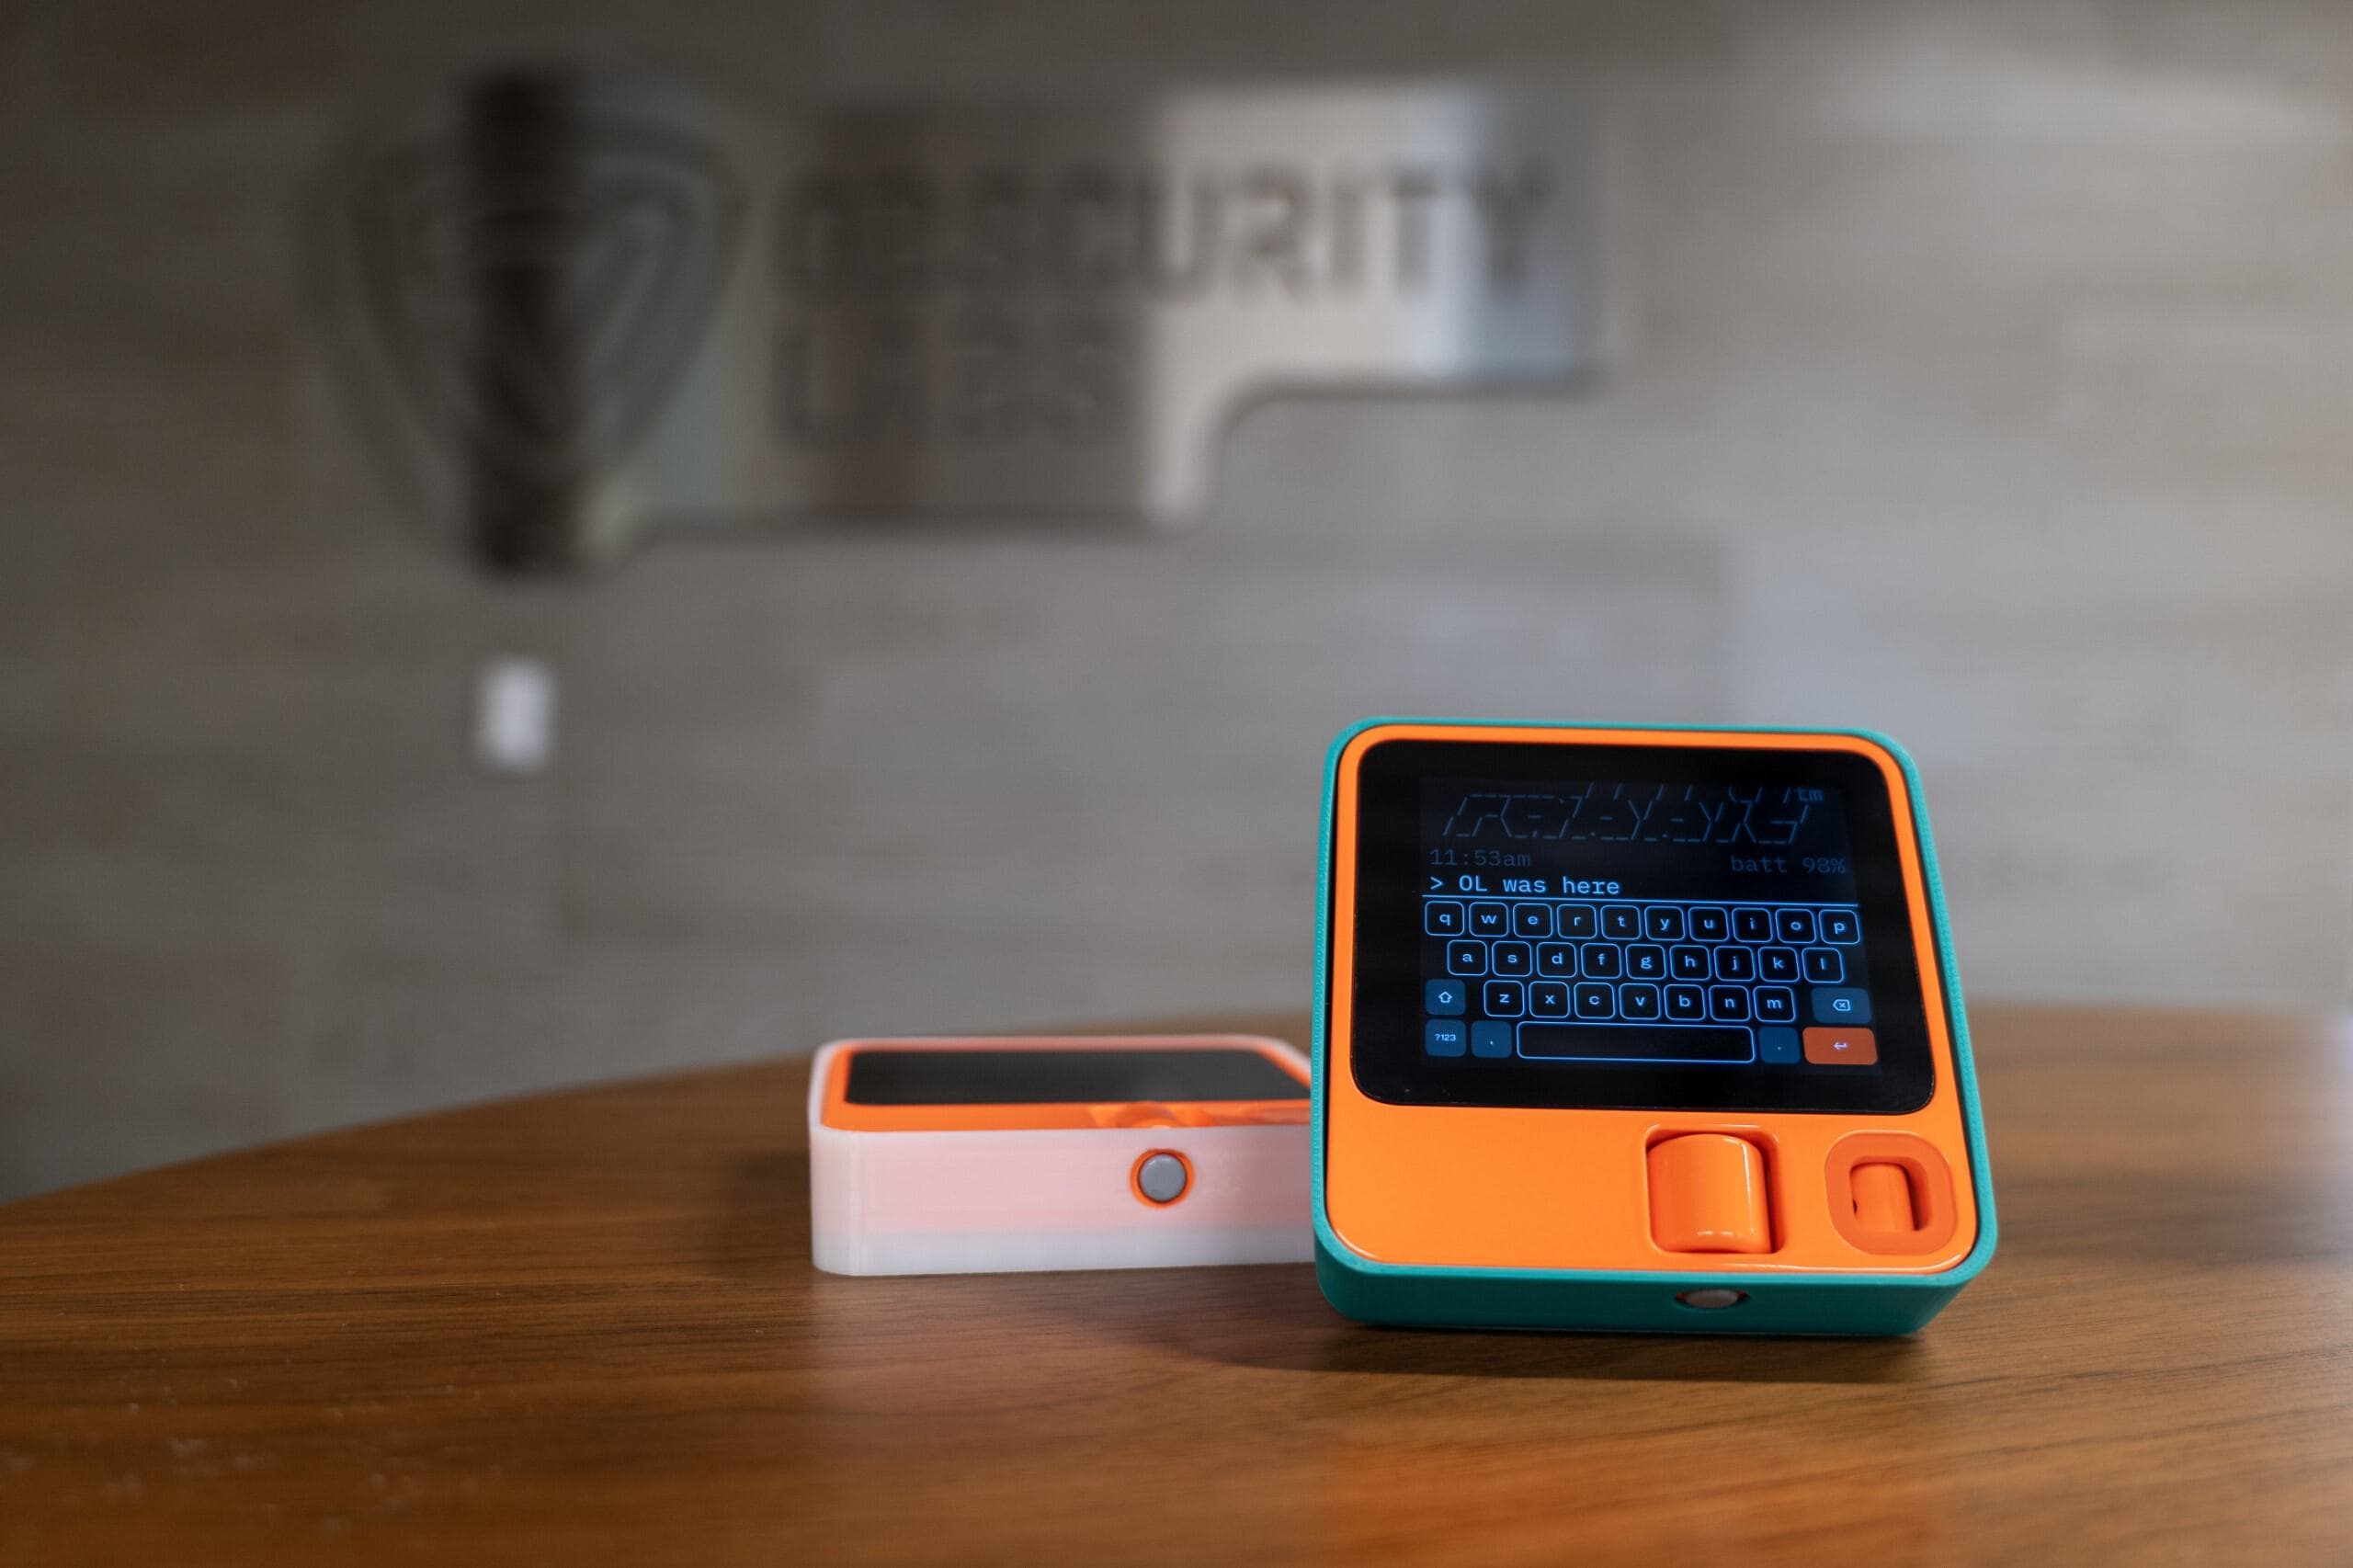
Product security
A published assessment of the R1 device and supporting services, covering attack paths, isolation boundaries, and findings.
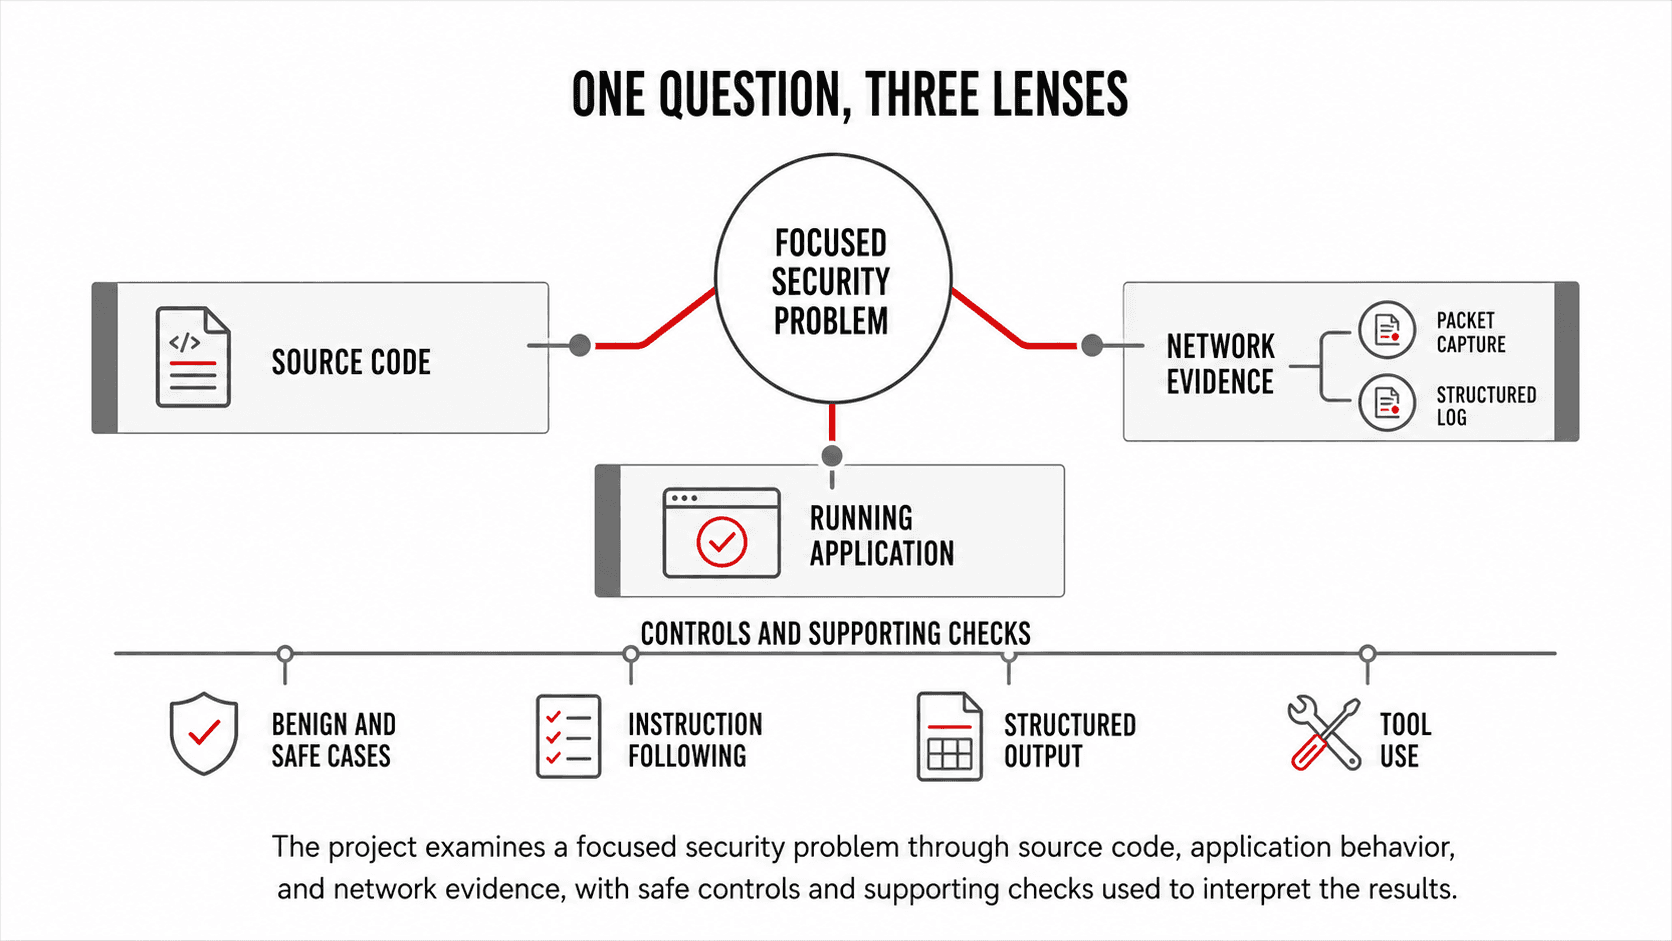
AI evaluation
How we built controlled evaluations around practical security tasks, tool permissions, repeatable evidence, and known limits.
Incident response
Contact our team to discuss investigation, containment, and recovery. Keep sensitive incident details out of the initial web inquiry.