Penetration testing & red team

Know what an attacker can reach.

We test applications, infrastructure, and trust boundaries to show how weaknesses connect—and what they put at risk. Manual testing, adversary emulation, and evidence your team can use.

The right engagement

Start with the question you need answered.

Assess a system, test an internal foothold, challenge your defenses, or work through detection gaps with your team. The objective sets the scope.

Engagement 01

Penetration testing

Where are the exploitable weaknesses?

A focused assessment of an application, environment, or release. We validate findings manually and connect weaknesses to their impact on the systems in scope.

  • Authentication, authorization, and business logic
  • Application, network, and cloud boundaries
  • Reproducible evidence and prioritized fixes

The handoff

Technical findings with exploit evidence, severity context, and remediation guidance.

Engagement 02

Assumed-breach assessment

What happens after the first foothold?

Start from an agreed point of access and test how far it can lead. Examine internal trust, privilege boundaries, and the controls intended to limit an intrusion.

  • Active Directory and identity controls
  • Lateral movement and privilege escalation
  • Segmentation and egress controls

The handoff

An attack-path map identifying reachable systems, failed boundaries, and hardening priorities.

Engagement 03

Red team operations

Can an adversary reach the objective?

An objective-led operation across people, processes, and technology. Threat-informed scenarios test both the attack path and how your organization detects and responds to it.

  • Reconnaissance and initial-access scenarios
  • Social and physical vectors when authorized
  • Detection and response observations

The handoff

An executive and technical attack narrative with control gaps and remediation priorities.

Engagement 04

Purple team validation

Can your defenders see and stop it?

Work alongside your security team to replay agreed adversary behaviors, inspect the available telemetry, and test detection and response changes.

  • Attack-path replay with the defensive team
  • Detection tuning and response runbooks
  • Retesting after control changes

The handoff

Documented detection gaps, tested improvements, and remaining validation work.
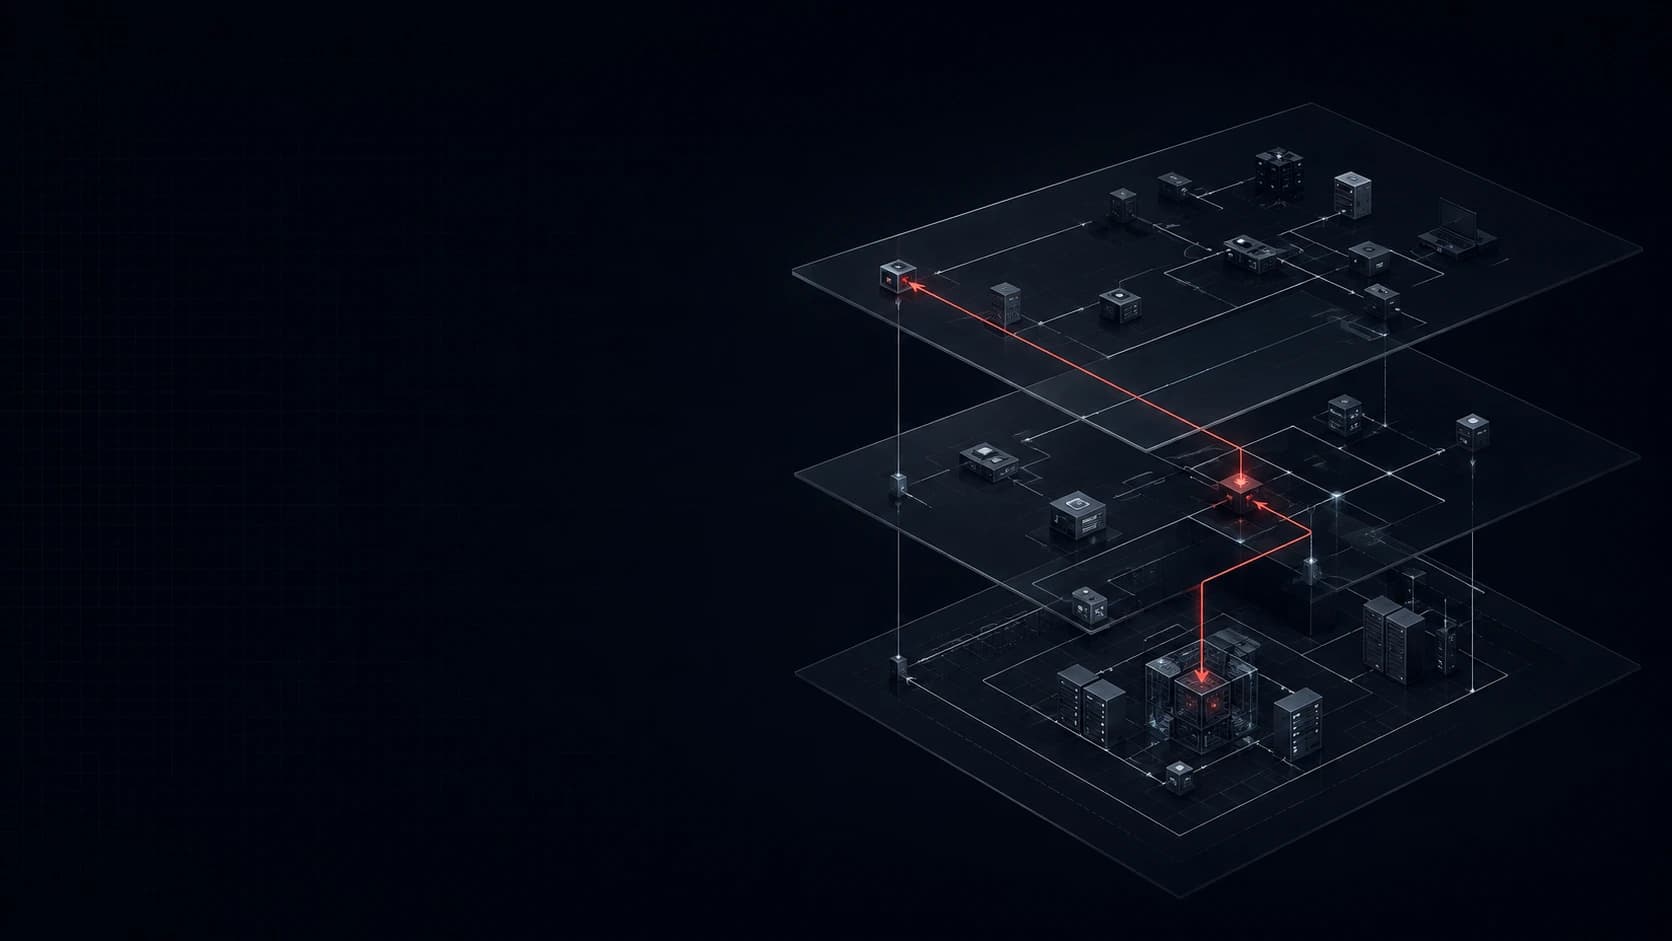
Scope, access, testing windows, and retest coverage are agreed before the engagement begins.

Testing coverage

Across the system.
Between the boundaries.

Test an individual surface or follow the connections across several. Each assessment is scoped to your environment and the access you authorize.

01

Web applications & APIs

Authentication, authorization, business logic, API trust boundaries, and sensitive data handling.

02

External infrastructure

Internet-facing services, exposed assets, and weaknesses that can create an initial access path.

03

Internal networks & identity

Active Directory, privilege boundaries, lateral movement, segmentation, and trust relationships.

04

Cloud & Kubernetes

IAM, workload isolation, secrets, CI/CD access, and orchestration control-plane risks.

05

Mobile applications

iOS and Android applications, backend APIs, local storage, session handling, and transport security.

06

Connected devices & IoT

Firmware, update mechanisms, device interfaces, protocols, and device-to-cloud integrations.

07

Hardware

Physical interfaces, debug access, storage extraction, and embedded security controls.

08

Wireless

Wireless access, rogue access points, encryption controls, and network segmentation.

09

Social engineering

Authorized phishing and pretexting scenarios that test human processes, reporting, and escalation.

Testing an AI-enabled system? Explore AI security

Operator-led assessment

Follow the path, not just the checklist.

Some weaknesses only become clear when you connect an application, an identity, and the infrastructure behind them. We build and adapt the tooling the assessment needs.

01

Manual attack-path testing

Our operators connect weaknesses across systems. Automation supports coverage; manual investigation tests business logic, identity abuse, and the paths between findings.

02

Onsite drop boxes

Purpose-built devices simulate an internal foothold under agreed rules of engagement. Test physical-to-network access, segmentation, egress, and defensive visibility.

03

Custom reconnaissance

We build OSINT collection and enrichment tooling to map asset and identity exposure, connect infrastructure relationships, and inform the assessment scenario.

Physical access, social engineering, and onsite devices are used only when explicitly included in the rules of engagement.

How we work

Controlled testing. Clear communication.

  1. 01

    Scope & authorize

    Agree on objectives, systems, access, exclusions, and rules of engagement. Establish testing windows, escalation contacts, and stop conditions before work begins.

    Outcome: Agreed scope and test plan.

  2. 02

    Test & coordinate

    Validate weaknesses, follow the paths between them, and capture evidence. Share findings during the engagement and escalate critical risks through the agreed contacts.

    Outcome: Validated findings and evidence.

  3. 03

    Report & validate

    Walk through technical findings and business impact with your team. Prioritize fixes and define the retest scope, timing, and criteria for checking remediation.

    Outcome: Remediation and retest plan.

What you receive

Evidence your team can work with.

Technical depth for the people making the fixes. Business context for the people making the decisions.

Executive risk brief
What was tested, what was reached, and why it matters to your operations. Clear priorities for leadership, including the limits of the assessment.
Technical findings
Affected systems, severity rationale, root causes, and recommended fixes for the people responsible for remediation.
Reproduction & evidence
Documented attack paths and supporting screenshots, logs, and technical artifacts so your team can reproduce and investigate the findings.
Remediation & retest plan
Prioritized actions, validation criteria, and an agreed retest scope. Record what has been addressed and where residual risk remains.
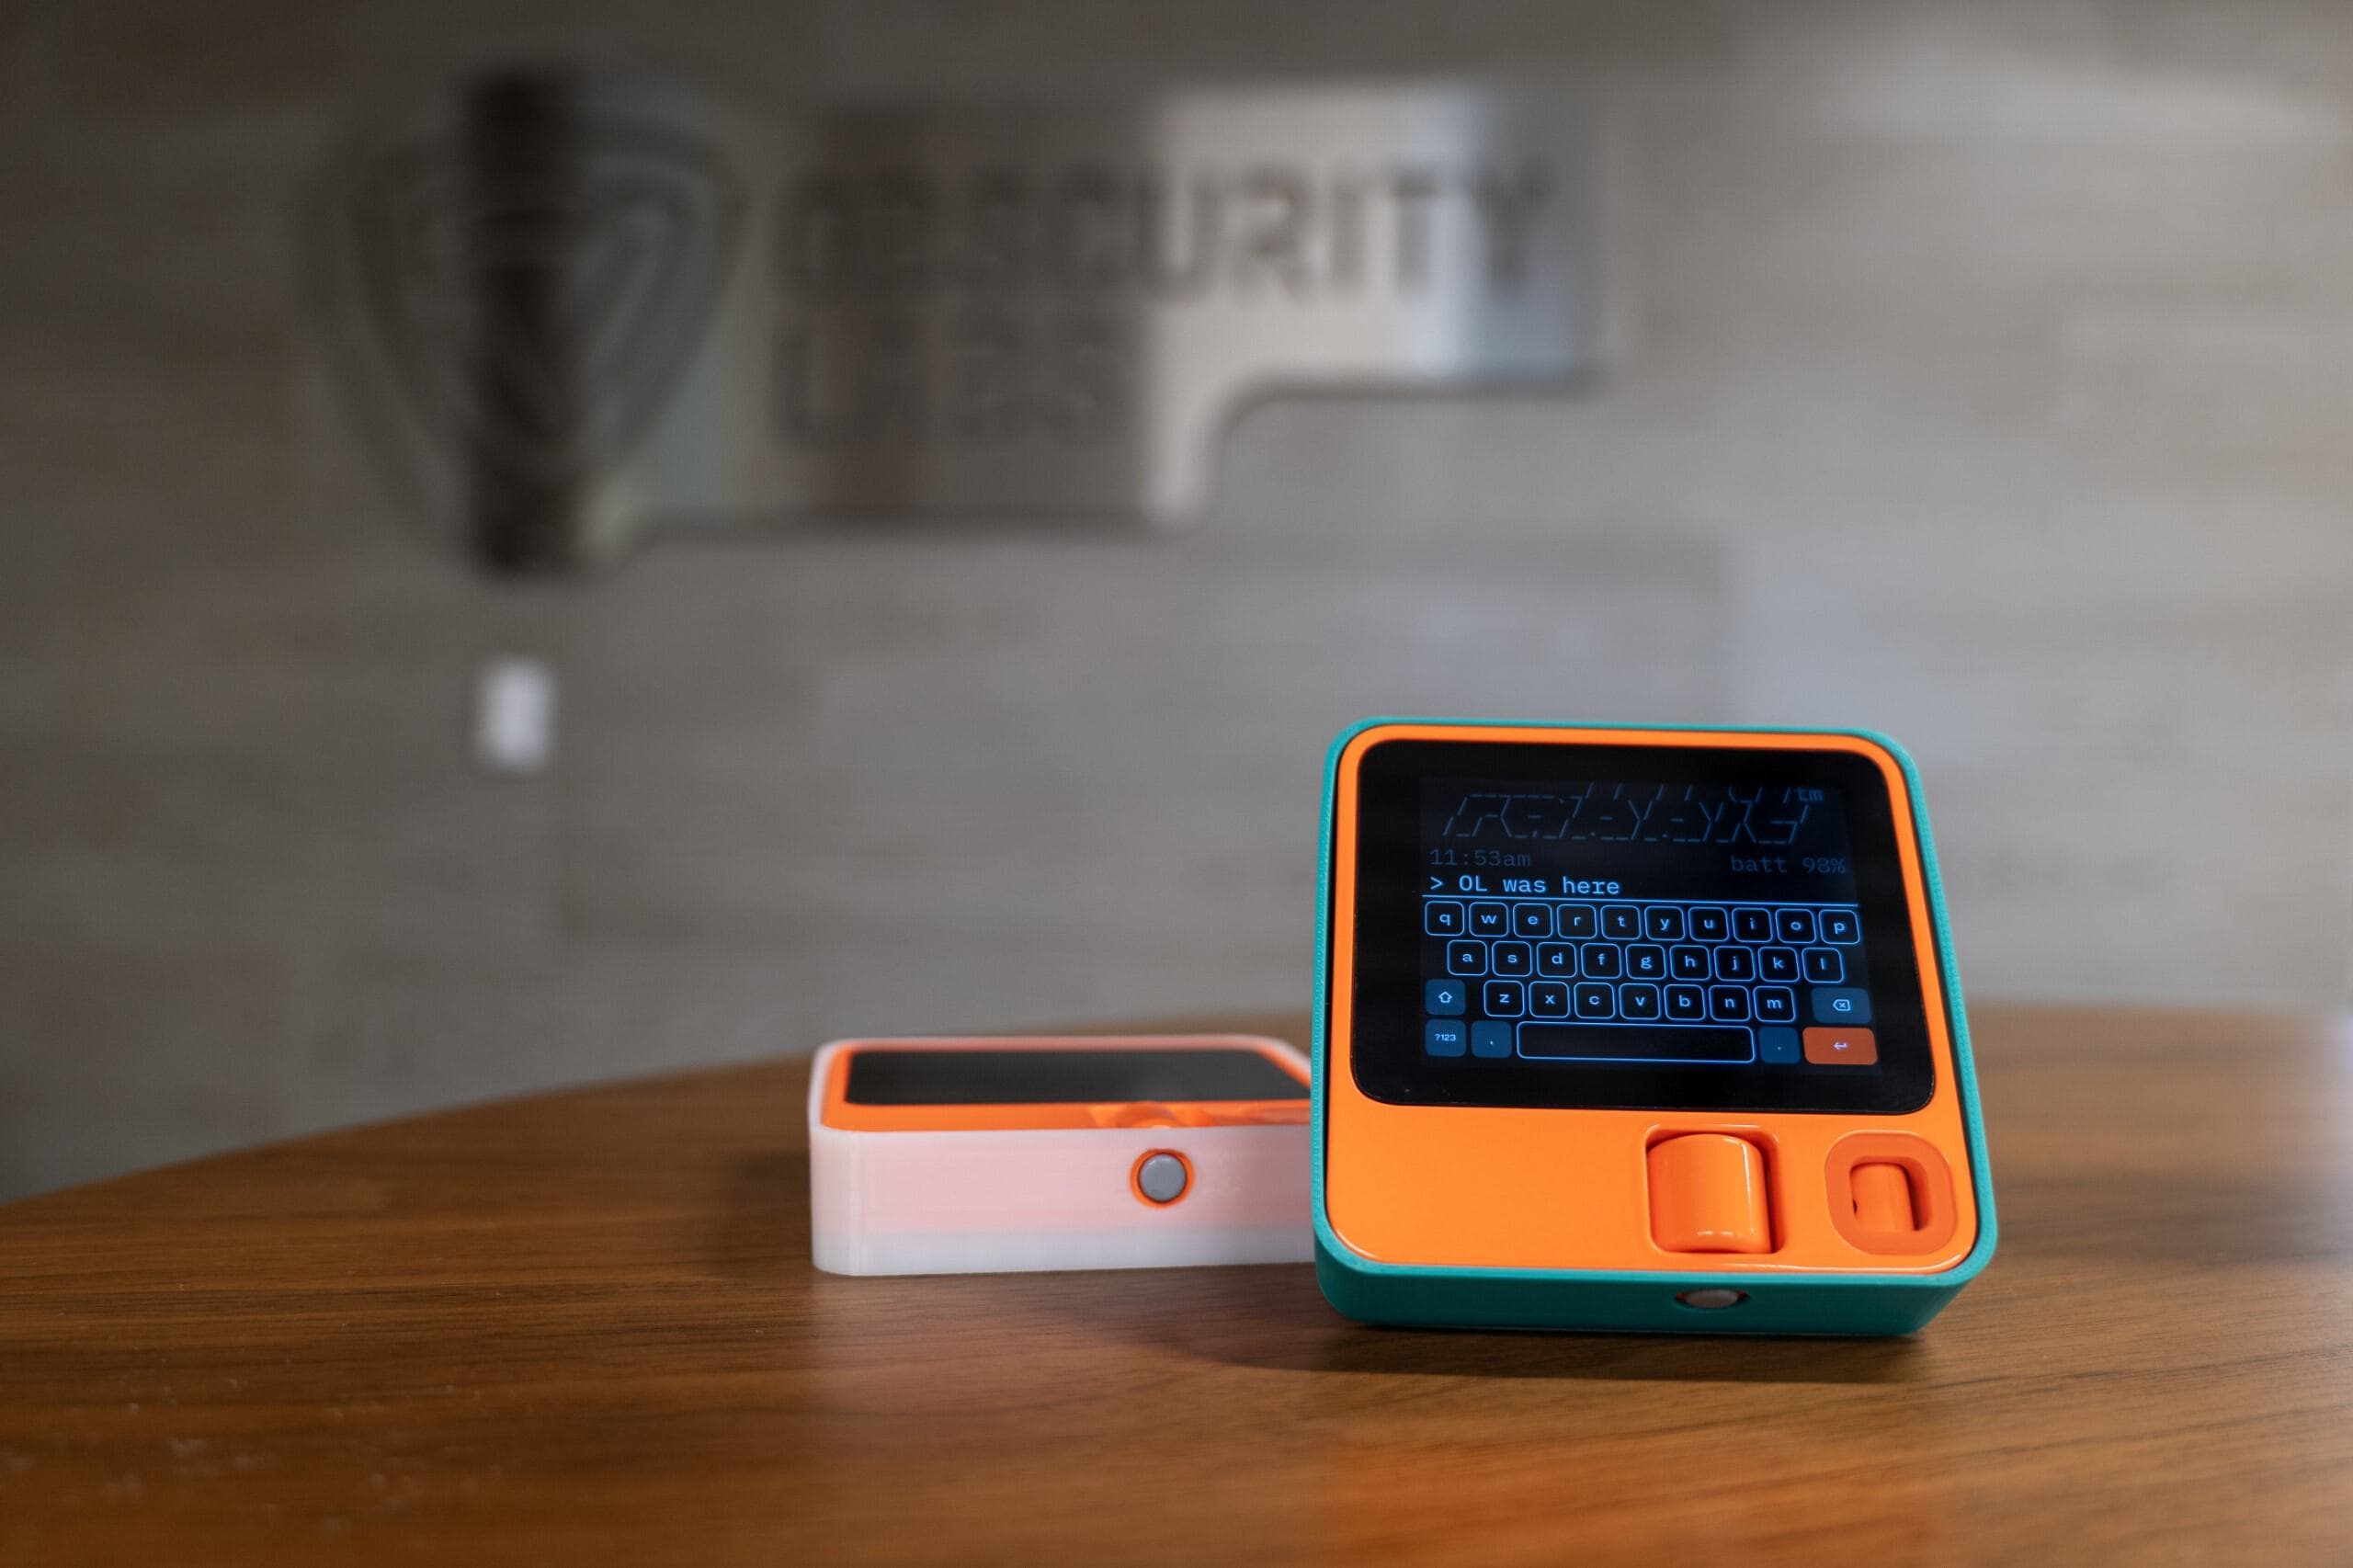
Obscurity Labs message displayed on a Rabbit R1 device during the assessment

From the field

Rabbit R1 penetration test

Our published assessment of the R1 device and its supporting services. Read the attack paths, findings, and context behind the results.

Before we begin

Plan the assessment.

Start with the systems in scope, the question you need answered, and your operational constraints.

Scope an engagement

Keep credentials and sensitive technical details out of the initial web inquiry.

Active incident? Get response support
Do we need a pentest or a red team engagement?

A pentest examines a defined set of systems for exploitable weaknesses. A red team engagement works toward an agreed objective and also examines detection and response. If the question is how far an attacker could move after gaining access, an assumed-breach assessment may be the right starting point.

Is this a vulnerability scan?

No. Scanning can support discovery and coverage, but the assessment includes manual validation, business-logic testing, and investigation of connected weaknesses. The report distinguishes validated findings from limitations and untested areas.

Can testing take place in production?

We agree on the environment, permitted techniques, testing windows, and stop conditions during scoping. Production testing needs explicit authorization and operational coordination. Activities outside the agreed scope are not performed without approval.

How long does an engagement take?

Timing depends on the number and complexity of systems, access requirements, objectives, and permitted testing windows. We establish the schedule during scoping rather than assigning the same duration to every assessment.

Does the engagement include retesting?

Retest coverage, timing, and any additional work are defined in the engagement scope. We establish validation criteria with your team so remediation can be checked against the original findings.

What should we share to get started?

Describe the systems you want tested, the reason for the assessment, and any deadline or operating constraints. Keep credentials, sensitive architecture, and vulnerability details out of the initial web inquiry. We can arrange the appropriate way to exchange scoping material.

Assessment references

References inform the agreed test plan; they do not imply certification or endorsement.